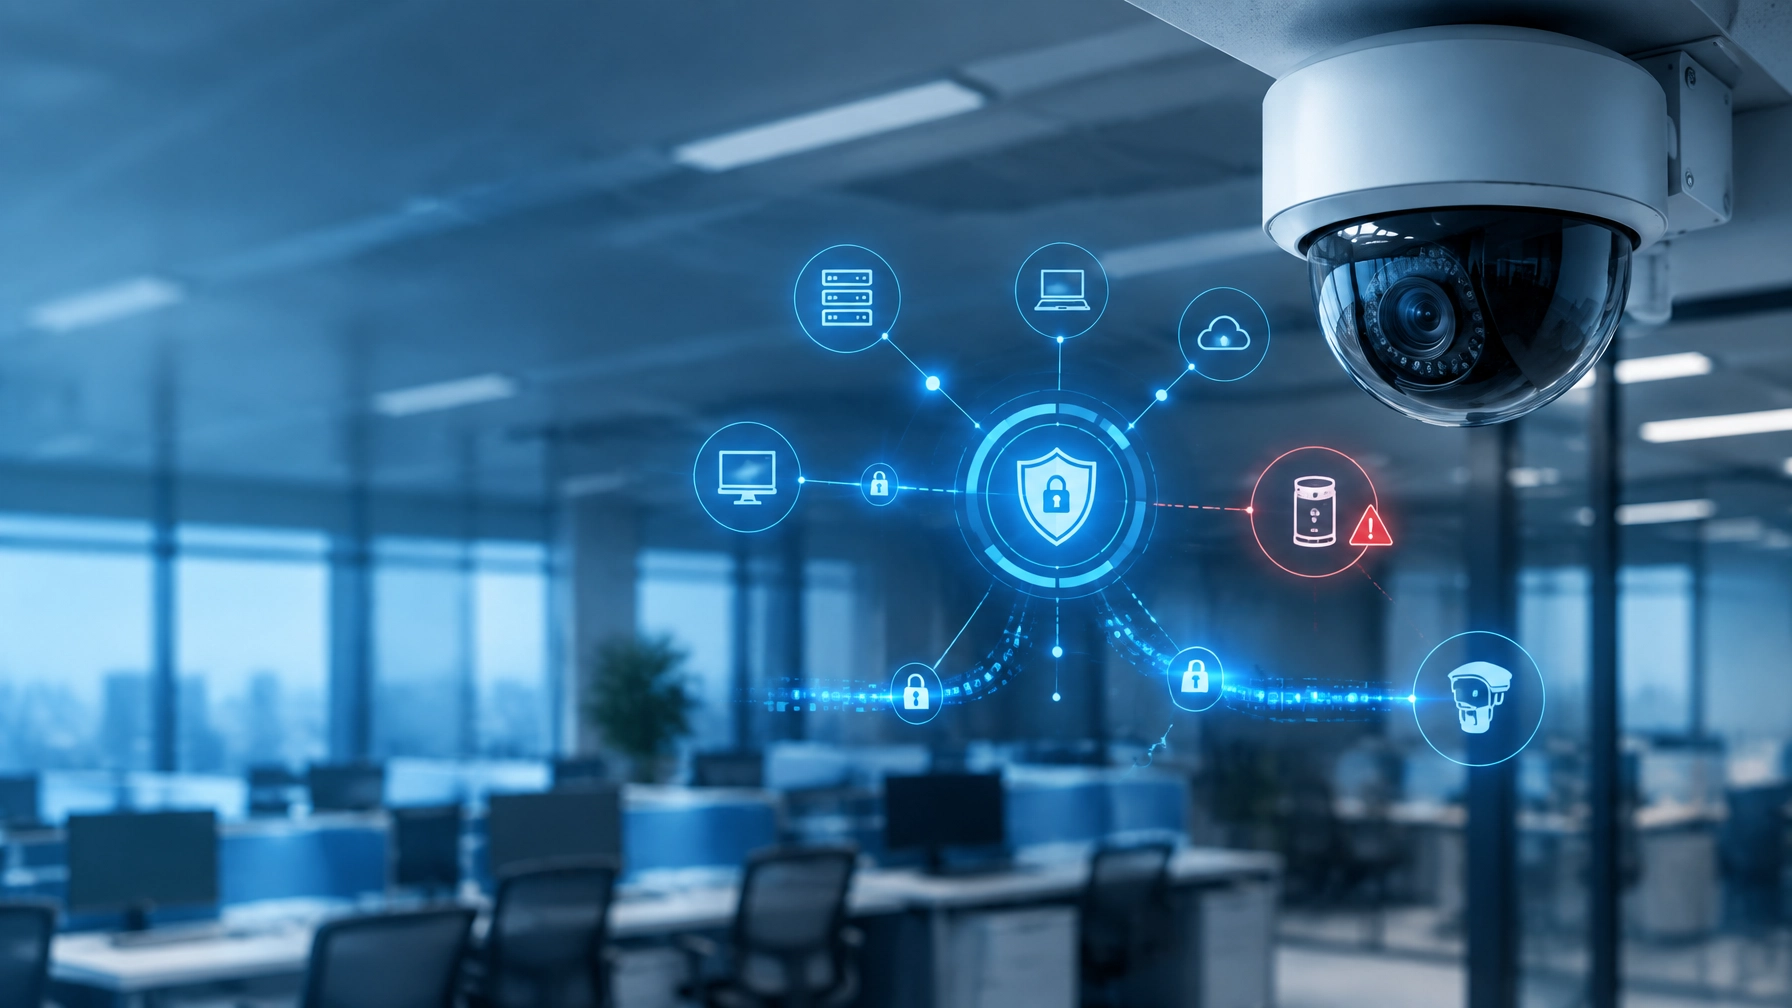
A security camera is supposed to help protect your business, not provide an attacker with a path into it. Yet that risk can develop when cameras, smart locks, door readers, thermostats, and other connected devices are installed for convenience and then placed on the same network as email, financial systems, patient records, or business applications.
This is the IoT blind spot: organizations invest in physical protection while overlooking the digital infrastructure that makes those devices work.
As part of Cybersecurity Awareness Month 2026 and ClearPath360’s weekly theme, The Smart Building Blind Spot: Securing the Devices That Watch Your Business, use this guide to evaluate whether your security technology is strengthening your defenses, or quietly expanding your attack surface.
“A camera can detect a threat outside your building while creating an opportunity for a threat inside your network.”
Begin by Understanding How a Camera Becomes a Cybersecurity Risk
Start with a simple question: What happens if someone gains control of one of your cameras?
The answer depends on how the device is configured and connected. An attacker may be able to view live video, access stored footage, change camera settings, recruit the device into a botnet, or use it as a foothold for exploring other systems.
The camera itself may not contain your most sensitive data. However, if it shares a flat network with workstations, servers, printers, wireless devices, or cloud applications, it may provide an attacker with a useful starting point for lateral movement.
Common weaknesses include:
- Default or reused administrator credentials
- Unpatched camera or recorder firmware
- Direct exposure to the public internet
- Unnecessary services such as Telnet or open RTSP access
- Weak vendor cloud account protections
- Shared passwords between cameras, recorders, and management platforms
- No centralized monitoring of unusual device activity
These issues are especially important for medical and dental practices in Genesee County. A compromised camera may not directly store protected health information, but a connected, poorly secured network could expose systems that handle patient scheduling, billing, email, or electronic health records.
Use CISA’s IoT security guidance as a baseline. The core message is practical: change default credentials, update devices, reduce internet exposure, and separate connected devices from critical business systems.
Check Whether Your Cameras Share a Network With Business Data
Next, map how your security devices connect. Do not assume that your installer, internet provider, or previous IT contractor documented the environment accurately.
Create an inventory that includes:
- Every camera and video recorder
- Door access systems and smart locks
- Environmental sensors and thermostats
- Wireless access points used by security devices
- Vendor cloud accounts and mobile applications
- Firmware versions and last update dates
- Users with administrative access
- Network segments, firewall rules, and remote access methods
Then identify what each device can communicate with.
If a camera can freely reach employee computers, file shares, Microsoft 365 administration systems, or a practice-management server, the environment is too permissive. A connected device should have only the network access required for its job.
This is where network segmentation for small business becomes one of the highest-value security improvements available. Place cameras and other IoT devices on a dedicated VLAN or subnet. Use firewall rules to control which management systems can access that segment. Block inbound internet access to camera interfaces, and use secure VPN or approved cloud access methods for remote viewing.

Segmentation does not make a vulnerable camera harmless. It limits what happens if the camera is compromised. That containment can be the difference between an isolated device problem and a business-wide incident.
Strengthen Credentials and Cloud Access
After mapping the environment, focus on identity. Strong IoT device security begins with eliminating credentials that attackers already know or can easily guess.
Begin by changing every factory-set password and any credential shared across multiple devices. Use a unique, long password for each camera system, recorder, administrative account, and vendor portal. Store those credentials in an approved password manager rather than a spreadsheet or shared document.
Separate administrative accounts from ordinary viewing accounts. Employees who only need to view footage should not be able to change camera settings, add users, export recordings, or modify retention policies.
Then secure the vendor cloud account:
- Enable multifactor authentication for every administrator.
- Remove former employees, installers, and contractors who no longer need access.
- Review user roles and limit permissions according to job responsibilities.
- Confirm that audit logs are enabled and reviewed.
- Set rules for downloading and sharing recorded video.
- Require secure access from managed devices whenever possible.
Cloud video can improve availability and simplify remote access, but it does not remove your responsibility for account security. A strong platform can still be undermined by a reused password or an unprotected administrator account.
For example, Eagle Eye Cloud VMS promotes encryption, multifactor authentication, role-based access, audit logging, and locked-down camera connectivity. Those capabilities can improve security, but they are only effective when your organization configures and manages them correctly.
Keep Firmware Current and Reduce Exposure
Now examine the software running on each device. Cameras are often installed and forgotten for years, even though their firmware may contain vulnerabilities that attackers actively search for.
Create a maintenance schedule that includes:
- Checking firmware versions at least quarterly
- Reviewing manufacturer security advisories
- Applying updates during planned maintenance windows
- Replacing devices that no longer receive security patches
- Disabling unused services and accounts
- Confirming that HTTPS and encrypted connections are enabled
- Reviewing router settings for port forwarding and UPnP exposure
A useful standard for security camera network security is simple: cameras should not be directly reachable from the public internet. If a remote viewer can connect through an exposed camera port, an attacker may be able to find that same entry point.
Security-focused manufacturers such as Axis Communications provide hardening guidance that emphasizes current AXIS OS firmware, signed software, strong credentials, HTTPS, and firewall protection. Review the Axis cybersecurity resources when evaluating an Axis deployment or planning an upgrade.
Remember that a reputable product is not a complete security strategy. Axis analytics, Eagle Eye cloud video, and other modern platforms can offer advanced protection, but they remain dependent on the network, identity controls, firmware process, and monitoring around them.
Treat AI-Assisted Surveillance as Part of the Security Architecture
As you evaluate AI-driven security surveillance, focus on more than detection accuracy. Ask how the platform is secured, updated, monitored, and integrated with the rest of your environment.
AI-assisted systems may identify people, vehicles, objects, unusual behavior, or activity outside normal schedules. These capabilities can help businesses reduce false alarms and respond more quickly. ClearPath360 has previously outlined how AI-powered surveillance can shift security from reactive monitoring to proactive protection.
However, intelligent analytics introduce additional questions:
- Where is video processed: on the camera, on-site, or in the cloud?
- What data leaves the building?
- Who can access analytic results and recorded footage?
- How long is video retained?
- Are software updates automatic, tested, and documented?
- Can the system integrate with access control and incident response?
- What happens if the internet connection fails?
Use this evaluation to connect physical security and cybersecurity rather than treating them as separate purchasing decisions.

Build a 360-Degree Protection Plan
A secure camera system requires more than a better camera. It requires coordinated management across devices, networks, identities, facilities, and people.
That is the purpose of a 360-degree approach. ClearPath360 brings managed IT services Michigan businesses can rely on together with cybersecurity protection and intelligent surveillance. The goal is not simply to repair a camera after it stops working. The goal is to identify weak configurations before they become incidents, monitor for suspicious activity, and keep the entire environment resilient as your business grows.
Use ClearPath360’s guide to integrating physical security with cybersecurity to consider how access control, surveillance, network monitoring, and incident response can work together.
For a small business, the first improvement does not need to be complicated. Begin with an inventory. Change credentials. Enable MFA. Update firmware. Segment the camera network. Remove direct internet exposure. Then establish a recurring review process so those controls remain effective.
“The objective is not to eliminate every connected device. It is to make every connected device accountable.”
Take the Next Step With a Security Assessment
Your cameras may be protecting entrances, hallways, parking areas, and sensitive rooms. Now confirm that they are not creating an unmonitored path into the systems your business depends on.
ClearPath360 can assess your cameras, access control devices, cloud video platforms, network configuration, firmware practices, and administrative access. We will help you identify gaps and prioritize practical improvements based on your operations, risk profile, and budget.
If your business is in Michigan or Genesee County, book a security assessment with ClearPath360 today. Proactive Genesee County cybersecurity starts with understanding every device connected to your business, and protecting the complete path from the front door to the network core.